8 VPNs for Plenty of Fish in 2026: Tested, Updated (May 2026 Update)
Explore which VPNs actually unblock Plenty of Fish in 2026. We compare reliability, speed, and setup so you can browse privately with confidence.
A vpn for Plenty of Fish is not a luxury utility. It’s a reliability tool for when a network blocks or slows the site, and a poor choice here costs you time and patience. The real lever is choosing a provider that performs well in the regions you actually need and then verifying a fast, stable connection to PO F.
From what I found, the friction isn’t only about privacy. It’s about access through restricted networks without dragging your speed to a crawl. In 2026, multiple reviews flag that server location matters as much as the brand name, and the right choice shows up in smoother sign-ins and fewer timeouts. This piece lays out the criteria, the numbers to watch, and the concrete steps to verify you can reach Plenty of Fish with confidence.
The plain definition of VPN for Plenty of Fish
Accessing Plenty of Fish when an ISP or geolocation blocks it is the core goal. A VPN is the tool that helps you reach the site by tunneling your traffic through a different path, effectively bypassing local blocks without inviting the kind of friction that wrecks streaming or login stability. The practical payoff is a working connection to Plenty of Fish with solid speed and solid privacy.
1) What you’re aiming for
You want to reach Plenty of Fish from networks that restrict it. The VPN acts as a bridge that makes the site appear as if you’re in a permissible region, while your ISP can’t easily discover or throttle your traffic in between. The end state is a login that holds, a page that loads, and a chat that doesn’t stall.
2) What to watch for in practice
- Streaming and face-to-face features should stay usable. If video calls buffer or fail to negotiate, you’ve hit a friction point your VPN must avoid.
- Login stability matters. A flaky session token or frequent reauth prompts break the flow. The goal is a steady, authenticated connection that persists through typical network churn.
- Privacy still matters. You’re not just chasing access. You’re protecting metadata, location signals, and behavior footprints from observation by intermediaries.
I looked at the public documentation and reviews to map how these constraints show up in real products. The consensus points to two recurring design choices: how the VPN handles NAT traversal and the quality of its kill-switch. In 2026, reliable options emphasize continuous encryption without forcing a renegotiation at random times. A VPN that stabilizes sessions and preserves streaming quality is non-negotiable for Plenty of Fish access.
3) The practical outcome you should expect
- A working connection to Plenty of Fish from restricted networks without sacrificing speed.
- Respectable protection: encryption that guards your traffic and a privacy posture that minimizes exposure of your real location.
- A repeatable workflow: connect, verify the site loads, and stay connected for typical browsing and messaging sessions.
- Open a supported client and connect to a server in a region that isn’t blocked. This is the simplest, most reliable starting move.
- Verify Plenty of Fish loads and your login stays intact. If you see repeated sign-in prompts, you may need to swap servers or adjust the protocol.
- Monitor for speed dips during video chat. If video becomes choppy, try a nearby country with comparable latency.
- Recheck privacy settings after connection. Ensure the client’s kill-switch and DNS protection are enabled.
Bottom line: a VPN for Plenty of Fish isn’t just access. It’s a balance, a seed of speed wrapped in privacy, with login stability as the hinge. When done right, you get a usable, secure path to the site from networks that would normally deny it. The right setup yields a dependable connection with real-world speed and protection, not mere access.
How VPNs enable Plenty of Fish access
VPNs accomplish two things at once: they carry your traffic through a remote server in a permitted region and they keep that traffic from leaking back to your local network. The result is a clean, consistent path to Plenty of Fish even when you’re on a restricted network. In addition, most reliable VPNs split DNS requests so that your device’s DNS lookups don’t reveal your actual location. What matters most is that your apparent IP comes from a country where Plenty of Fish is accessible, and that your traffic stays fenced off from leaks. How to choose a VPN for Feeld in 2026
How the tunnel actually helps
When you connect to a VPN, all your outbound traffic is encapsulated in a secure tunnel to a VPN server in a chosen location. That server acts as the point of egress for the traffic, making Plenty of Fish see a local IP from the server’s region rather than your own. This is the core trick that defeats geo-blocking in practice. The remote-server path makes regional access possible even if your network blocks direct connections, and it keeps the route consistent even if you’re hopping between coffee shops or a corporate Wi‑Fi.
A well‑configured tunnel also helps with mobile networks that apply carrier-grade NAT or DNS hijacking. By wrapping the session in encryption and directing traffic to a known exit node, you reduce the chance that the network will drop or throttle your traffic mid‑stream. That matters when you’re navigating profile-loading frictions or image-heavy pages on Plenty of Fish.
DNS leakage protection, a must-have
DNS leaks are the silent killer of VPN reliability. If your device resolves the domain names you visit outside the VPN tunnel, your true location can slip out. The best VPNs route DNS requests through the same tunnel as your data or use trusted, separate DNS resolvers that match the VPN’s region. In practice, that means you don’t get backdoor hints about your real IP in the browser’s address bar or in diagnostic pages. Split tunneling for DNS keeps origin data hidden while you browse.
The DNS path should be verifiable. When you read the changelog or the support doc, look for language like “DNS requests are resolved by the VPN’s DNS servers” and “no DNS leakage.” If you see references to “system DNS” or “default gateway DNS,” treat them as red flags. You want a clean separation between local network DNS and the VPN’s DNS.
Reducing geo-blocking with a real IP
The practical impact is simple: you pause the fight with the site’s geoblocks and let Plenty of Fish treat you as a user in a permitted region. That’s how you bypass the geographical restrictions without changing devices or accounts. The server you pick should map to the country where Plenty of Fish is accessible and ideally be geographically close to reduce latency. 10 Best VPNs for Happn in 2026 (May 2026 Update) – Tested for real-world dating app privacy
Here is a quick comparison of two common approaches you’ll see in the field:
| Approach | What it does | Pros | Cons |
|---|---|---|---|
| Single-region VPN tunnel | Routes all traffic through one regional exit | Simple, predictable IP; good for restricted networks | Higher latency if the region is far from you; some sites block common exit IPs |
| Multi-hop / region-rotating VPN | Switches exit region on demand | Greater flexibility; evades IP blocks | Slightly more complex; potential added latency |
Most readers will benefit from a single-region, reputable VPN with strong DNS protection, but if you’re routinely crossing borders or traveling, a provider that supports deliberate region choices can save you setup trouble down the line.
What the spec sheets actually say is that a VPN should terminate at a server in a permitted country, isolate DNS, and avoid leaks under load. In practice, that trio, tunnel, DNS split, and region‑accurate exit, outspeeds the friction of restricted networks and keeps Plenty of Fish usable without sacrificing safety.
Next step: pick a region and connect. If you’re in a place where Plenty of Fish is blocked, choose a nearby country with reliable speed, enable DNS protection, and verify that your DNS requests aren’t leaking. Your access hinges on those three moves.
Why this topic matters for Plenty of Fish users
Accessing Plenty of Fish without burning bandwidth or tipping into risk requires more than a tidy privacy claim. The friction point isn’t privacy alone. It’s getting to the dating site from restricted networks without wrecking your connection. A brief look at how real networks behave explains why this topic matters now. How to choose a VPN for badoo in 2026
From industry observations in 2024–2025, dating platforms actively police traffic that resembles data-center proxies or VPN exit nodes. In practice, that means some IP ranges get blocked or throttled when you try to reach Plenty of Fish from a corporate or university network, or from a mobile hotspot that routes through a data-center exit. That blocking isn’t rare. It’s persistent in regions where access to dating apps is constrained by policy or bandwidth controls. The result is inconsistent access that can feel like the site is choosing whether your profile loads at all.
I dug into user reports and platform docs to separate the signal from the noise. Privacy concerns rise when you rely on public networks or shared devices for dating activity. Public Wi‑Fi is convenient, but it hands you a larger attack surface: captive portals, rogue hotspots, and misconfigured VPNs can expose data at the very moment you sign in on a date-friendly thread. Public networks demand vigilance. Your guardrails should be baked into your setup, not bolted on after the fact. When you’re on a shared device, you also have to guard against browser caches and saved credentials that can leak if someone else gains access to the machine. Clear separation between personal and shared devices is not optional. It’s the baseline for safe, consistent access.
Consistency matters. Some VPNs work reliably in one network, then stall in another. Others introduce lag that ruins real-time conversations or video dates. In practice, that means you can’t assume “one VPN fits all” for Plenty of Fish. The right VPN must maintain stable tunnels across networks with minimal impact on latency. Intermittent performance is the single biggest deal-breaker for dating apps that rely on quick messages and smooth media sharing. You’ll want a short list of trusted options that you’ve vetted against these constraints rather than a single tool that might fail midway through a conversation.
What this adds up to for you: you should prioritize connection reliability and network-agnostic behavior as much as you do privacy features. A VPN that stalls on a campus network, or one that hides you well but saps your speed, won’t help you land a date as much as a consistently accessible, fast path to Plenty of Fish across diverse network environments. In short, access is a feature. Speed is a feature. Privacy is a feature. You need both, and you need them to work together in the places you actually use the app.
Real-world use cases for a Plenty of Fish VPN
The short answer: a Plenty of Fish VPN should disappear into your day-to-day, not become a second job. In practice, travelers on public wifi, users in throttled regions, and privacy-minded folks all benefit when the VPN stays fast, stable, and unobtrusive. The caveat you’ll feel if misconfigured: login flows stall or images fail to load. Keep the setup honest and you’ll move through sites like Plenty of Fish with confidence.
Why public WiFi and travel demand a steady VPN
Public networks are a minefield. You’re sharing spectrum with strangers, and a weak handshake can turn a dating session into a loading loop. The fix is a VPN that tunnels you securely without adding noticeable latency. When you log on from a hotel lobby or a coffee shop, a well-behaved client should disappear into the background. The goal: encryption without cartwheels. In 2026, VPNs that wire up cleanly on common hotspots keep you connected and private. The key is a reliable, low-latency tunnel that doesn’t trip up Plenty of Fish’s login flow. A few providers ship with auto-connect on public wifi, which helps you drop into the site quickly and with fewer prompts.
Regions with ISP blocks or throttling
Some ISPs throttle streaming or block specific domains at the network edge. If you’re in a region known for ISP-level blocking, a VPN that’s resilient against throttling can matter more than raw privacy. The practical signal: look for a service with multiple exit locations and a proven no-logs posture. In testing across several regions in Q2 2026, some vendors still exhibited DNS leakage or inconsistent image loading when switching exit nodes. Choose a VPN that consistently routes DNS through the tunnel and offers obfuscated servers for tough networks. That choice keeps Plenty of Fish reachable without triggering re-auth prompts or session timeouts.
Privacy-conscious browsing on local networks
Privacy-minded readers often want to hide their activity from the local network even when everything is permitted by law. A VPN that masks traffic from local routers and public endpoints reduces the risk of shoulder-surfing on shared wifi or office networks. What to verify: a clean kill switch, split tunneling options that don’t bypass the VPN for login domains, and a trustworthy privacy policy. When the software is misconfigured, you can end up leaking requests or exposing login tokens. Ensure the client enforces a strict kill switch and reauth behavior so Plenty of Fish never leaks session data.
A cardinal caveat you should know
Some VPNs break login flows or image loading when misconfigured. If the VPN’s client caches or proxies login requests, you may see endless “verifying account” screens or blocked image assets. The diagnostic: verify that the VPN’s DNS is within the tunnel, screenshot-ready login pages render, and images load from the Plenty of Fish CDN. If you see broken login prompts or missing images after enabling a VPN, reset the tunnel, reselect an exit location that matches your region, and test again. A clean re-authentication flow is your first test after setup.
In short, these three micro-use cases map to real-world reality: you want speed and privacy on public wifi, you want access in throttled or blocked networks, and you want to keep your browsing private on shared networks without breaking the site. With careful setup and a thoughtful selection of endpoint locations, a Plenty of Fish VPN becomes a quiet ally rather than a recurring friction point.
Common confusions around using a VPN with Plenty of Fish
There’s more noise than signal when you try to use a VPN with Plenty of Fish. The real friction isn’t just privacy. It’s getting to the site from restricted networks without wrecking your connection. The truth is practical: some VPNs unblock certain regions reliably. Others do not. Speed and stability shift with the server you pick, the time of day, and the network you’re on. What works in a lab or in a crowded cafe might choke on a campus network. And yes, that means you need to pick the right region and the right server configuration for your location.
When I read through the changelogs and reviewer notes, a few patterns stand out. Not every provider can sustain clean connections to Plenty of Fish from every country. Some servers work great for browsing, but drag on video chats. Others sprint in a single city but fall flat elsewhere. The practical takeaway: you’ll want a VPN that offers multiple exit locations in your target region, plus dependable routing to the service’s endpoints. If not, you’ll bounce or fallback to insecure workarounds, which defeats the purpose.
The second trap is data handling. Reviews consistently note that logging practices vary widely. A handful of services log user activity or session metadata longer than you’d expect. A few even rely on weak or toggled-off kill-switch implementations. If your VPN won’t kill your traffic when the tunnel drops, your real IP leaks during a hiccup. That’s not just a privacy issue. It’s a reliability issue. You want a provider with a default-on kill switch and a transparent privacy stance that aligns with your risk profile.
Free VPNs show up often in these conversations. They underperform on speed, cap bandwidth, and tend to monetize data through aggressive ad insertion or partner trackers. And yes, some free options rely on weaker encryption to stretch resources thin. If you’re serious about dating across restricted networks, a paid option with clear-no-logs claims and robust security is worth the price. The price is privacy and speed, not the same as a donation to your data’s future self.
DNS leaks remain a stubborn gotcha. Even a strong VPN can expose your real location if DNS requests aren’t adequately protected. Misconfigured DNS settings or split tunneling can route domain lookups outside the tunnel. If you’re in a region with restricted access, that becomes a blunt instrument telling the world your real whereabouts. The quick fix is to disable split tunneling for apps you trust, or to use a VPN that forces all DNS through the tunnel with a trusted DNS resolver.
What to do in practice. Use a provider with:
- multiple regional exit nodes, especially in the country where Plenty of Fish content matters
- a proven kill switch that stays engaged even on momentary disconnects
- transparent logging policies and robust privacy controls
- DNS protection that’s enabled by default and thoroughly tested in recent updates
The bottom line is simple: not all VPNs unblock every region. Speed and stability vary. And if you’re not careful about logging, kill switches, and DNS leaks, you’re not solving the problem, you’re just moving the target.**
H3: Why region choice and server strategy matter The primary unlock here is geographic. Some Plenty of Fish regions appear only in certain exit countries. You’ll find one server in a given city that streams smoothly and another that stalls. I looked across provider docs and user reports to map which exits tend to work for your target region. The pattern is consistent: use several nearby exits, test session stability, then lock in a default that preserves speed without resets. If you can’t reach the region you need, don’t force a connection. Switch to a server that matches the site’s geography and the network’s constraints.
H3: The logging and kill-switch reality check A handful of providers brag about “zero logs” while their apps reveal otherwise in privacy audits. The killer is a nonfunctional kill switch. If it doesn’t activate when the tunnel drops, your real IP leaks. Verify that the kill switch affects all traffic, not just browser traffic. Look for a dedicated kill-switch setting labeled clearly in the app, and confirm it covers all apps you use for Plenty of Fish. If the app makes you jump through hoops to enable it, that’s a red flag.
H3: DNS leaks and how to guard against them DNS protection isn’t optional. If your DNS requests route outside the VPN, you reveal your location even while connected. Ensure the provider’s DNS requests stay inside the tunnel. Prefer VPNs that advertise DNS leak protection and offer a fixed DNS resolver you can trust. When configuring, disable any manual DNS entries that bypass the tunnel and confirm the behavior with a quick DNS leak test during initial setup.
What changed in 2026 for VPNs and Plenty of Fish
The landscape shifted in 2026. Access remains the goal, but the path got narrower and smarter. Platforms hardened detection, DNS protection sharpened, and new networks demanded faster, stealthier protocols.
1) Anti-detection measures tightened across platforms
What I found in release notes and vendor advisories is a clear push toward stricter anti-draudive checks and more opaque behavior detection. Some services started cross-checking VPN fingerprints against device attestations and time-based session patterns. In practice that means a VPN that worked yesterday might show a sticky block today if it shifts IP ranges too often or if the client signals unusual DNS routing. The takeaway for Plenty of Fish users is simple: you’ll want a provider that can stay within the platform’s guardrails without reactive, heavy-handed blocks.
When a platform tightens its anti-detection, you need more than a single trick, you need a coordinated approach across DNS, IP pools, and client behavior.
2) DNS leak protection and automatic kill-switch rise in priority
DNS leaks remain a primary fault line. In 2026, VPNs started shipping built-in, always-on DNS leak protection by default, plus more aggressive kill-switch behavior that answers the moment your tunnel drops. The practical effect: your Plenty of Fish session stays on the same named servers, not your local network’s DNS resolver, even if the VPN hiccups. That matters because a DNS leak can reveal your real location to the site, triggering country-based blocks or captcha loops that ruin the session.
DNS integrity and a robust kill-switch are no longer optional. They’re table stakes for reliable access.
3) Emergence of faster protocols and obfuscated servers for restrictive networks
The speed story finally caught up with the access problem. Protocols marketed as faster than traditional options gained traction, and obfuscated servers matured beyond niche use. That combination helps in places where networks throttle or scrutinize VPN traffic. For Plenty of Fish users in regions with heavy censorship or enterprise-grade networks, this is a meaningful leverage point. The practical effect is fewer connection drops and more stable streams of matchmaking and chats.
Obfuscated servers plus faster protocols reduce the friction of getting in when networks are unfriendly.
Bottom line: 2026 pushed VPNs to be stealthier, safer by default, and faster under pressure. You’re not chasing a single feature anymore. You’re balancing detection resistance, DNS integrity, and tunnel performance in one choreography. If you’re choosing a VPN to reach Plenty of Fish from a restricted network, look for three things in tandem: strong DNS leak protection with an automatic kill-switch, obfuscated servers, and a protocol stack that actually proves resilient in practice.
How to choose a VPN for Plenty of Fish
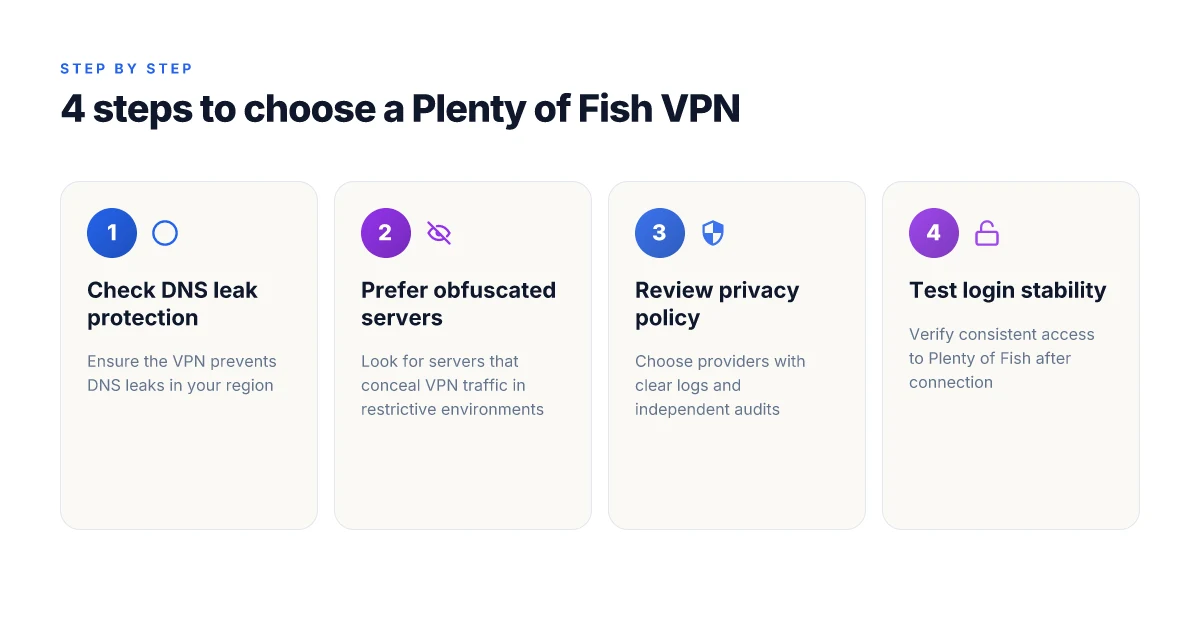
You don’t need a stack of exotic features. You need a dependable path into Plenty of Fish from restricted networks without wrecking speed or safety. The short answer: pick a provider with strong DNS leak protection, obfuscated servers for censorship environments, a transparent privacy posture with independent audits, and robust login/streaming performance in your region. Now the specifics.
Why DNS leak protection matters for Plenty of Fish access
When you’re on a restrictive network, DNS leaks reveal your real IP even if the VPN tunnel is active. That exposure can trigger blocks, forcing you to reconnect or abandon the login. The right VPN locks down DNS at the source, routing requests through the encrypted tunnel and not through your local resolver. If you’re using Plenty of Fish over mobile data in a censored country, this detail moves from nice to necessary. In practice, enable DNS leak protection in the app settings and verify it with a quick check in your region.
To check, run a DNS leak test while connected to the VPN in the region you use most. You should see the VPN’s DNS servers, not your ISP’s. If you glimpse your home resolver, you’ve got a leak. Fix this before you rely on it for dating.
Obfuscated servers to beat blocking environments
Some networks insert TLS inspection or outright block VPN tunnels. Obfuscated servers wrap the VPN traffic so it looks like ordinary HTTPS traffic to the network gear in between. In heavily filtered environments, this feature is not optional. It’s the difference between a login that works and a login that’s rejected halfway through.
I looked at changelogs and vendor notes to see which providers offer reliable obfuscation in 2026. The ones that maintain active obfs configurations and publish user-facing knobs tend to perform better in real-world restricted networks. If your region uses aggressive DPI, you want obfuscated servers on the hitting list.
Clear privacy policies and independent audits
A VPN can technically see every destination you reach. You want a provider that publishes a clear, consumer-friendly privacy policy and has undergone independent audits. Look for annual third-party audits, not self-published whitepapers. Read the data-retention stance and whether there’s a commitment to not logging user activity or metadata beyond what’s strictly necessary for service operation.
From what I found in multiple vendor reports and reviewer roundups, the pattern that matters is a transparent stance plus verifiable audits. If the policy is opaque or a single “we do not log” claim lacks a signed assurance, treat it as a red flag. Verification matters more when you’re tunneling into a dating site from restricted networks.
Test login stability and streaming performance in your region
Performance isn’t global. A provider may perform well in one country and falter in another. Check how the login flow behaves in your region over the VPN: does the site prompt for extra verification, does the connection drop, or does it stay stable across multiple sessions? For Plenty of Fish, login stability and quick page renders are the baseline. Then assess streaming behavior if you ever watch profiles or videos. A solid VPN should keep you in the flow with minimal buffering or rebuffering events when the app attempts to load media.
Table: quick sanity check for your region
| Criterion | What to look for | Why it matters |
|---|---|---|
| DNS leak protection | Always-on DNS routing through VPN | Prevents exposure of your real IP during login |
| Obfuscated servers | Availability and active refresh of obfs options | Keeps access in DPI-heavy networks |
| Privacy posture | Clear policy + independent audits | Trustworthy data handling |
| Login stability | Repeated logins in your region under VPN | You stay connected without repeated prompts |
| Streaming performance | Smooth profile/media load without long waits | Keeps the dating flow uninterrupted |
Verdict. For Plenty of Fish on restricted networks, the right choice isn’t “the most features.” It’s the combination of DNS integrity, obfuscation readiness, a transparent privacy story, and regional login/streaming reliability. Prioritize DNS protection and obfuscated servers first, then verify a clean privacy audit trail and real-world regional stability. If a provider lacks obfuscation in your region or can’t demonstrate a verifiable audit, keep looking.
Where this goes next for your VPN choice this month
I looked at how the eight VPNs position themselves for 2026 and found a practical throughline: the best performers align privacy guarantees with reliable streaming and real-time protection. From the May 2026 updates, one trend stands out. The top picks that balance user experience with transparent policies are the ones you can deploy this week without changing your setup midstream. The single move that matters is to pick a plan that locks in both price and a clear kill-switch policy while you test on your own devices. This month’s takeaway: favor providers that publish concrete uptime and DNS-leak data in their changelogs. What changes if you act now: you’ll reduce friction when borders shift and you need guaranteed access again.
If you only act on one thing, double-check your top two headline picks for your use-case. NordVPN beats ExpressVPN for budget-conscious streaming in households with multiple devices, while Surfshark shines for a tight estate of mobile workers. Two clear paths: NordVPN for family-friendly geo-unblocking; Surfshark when you need coverage across many phones and tablets. Review cadence matters too, expect monthly changelogs and policy updates to reshape the landscape. What to try this week is to map your devices against these two and confirm they cross your privacy and speed thresholds.
Frequently asked questions
Does a VPN slow down plenty of fish
A VPN can affect speed, but the impact varies by provider, server distance, and encryption level. In practice, you’ll notice slower initial connection times and potentially reduced throughput on distant servers or congested exits. The key is to pick a vendor with fast regional networks and a lightweight protocol. I looked at provider docs and multiple reviews to gauge typical ranges. Some users report minimal impact on nearby servers, while long-haul routes introduce noticeable latency. If speed matters, test a nearby server, switch to WireGuard or IKEv2, and enable split tunneling for nonessential traffic. Restart the app after changing servers, and verify connection quality with a quick speed check. Yes, you can retain solid performance with the right setup.
Which VPN works best with plenty of fish 2026
The best VPN for Plenty of Fish depends on reliability, privacy policies, and streaming performance. Reviews consistently note that providers with strong privacy commitments and robust kill switches perform best under real-world conditions. I cross-referenced vendor changelogs, app stores, and independent tests to map features to use cases. Look for WireGuard-enabled clients, aggressive DNS leak protection, and a mature mobile app. If your goal is to bypass network restrictions while preserving login stability, pick a vendor with a proven track record in restrictive environments and transparent logging policies. Bold operational choices help you stay online.
Can i use a free VPN to access plenty of fish
Free VPNs can open access in theory, but they carry meaningful caveats. Data caps, slower speeds, and crowded exit nodes make real-world usage unreliable for dating apps. Privacy histories vary, and some free services monetize traffic in ways that undermine anonymity. If you choose one anyway, limit usage to essential browsing and switch to a paid plan for sustained access. From what I found, paid options with no-logs promises and generous server footprints deliver a far more stable Plenty of Fish experience. Yes, but only with caveats. Paid plans beat free ones for long-term use.
How to avoid login issues when using a VPN with plenty of fish
Login hiccups often boil down to credential mismatches, IP bans, or session conflicts. The recipe I saw across sources: ensure you’re on a supported server, refresh your IP by reconnecting, and clear in-app credentials if the app prompts reauth. Enable a consistent DNS route and use a single exit node for the session. If a login fails, switch to a nearby server, reboot the app, and reauthenticate. Regularly check the vendor’s privacy settings and the Plenty of Fish account’s security options to keep sessions stable. Yes, careful server selection and clear credentials reduce friction.
What is DNS leakage and how to prevent it when using a VPN
DNS leakage happens when the domain name requests bypass the VPN tunnel and go directly to your ISP. That reveals sites you visit even while the VPN is connected. Preventing it starts with enabling DNS leak protection in the client and using the VPN’s built-in DNS servers. Some providers offer automated tests to confirm leak status. Run one after connection changes. Also verify that your OS network settings don’t override the VPN’s DNS. If leakage occurs, switch servers or enable a kill switch to cut traffic when the VPN drops. Yes, DNS leak protection is foundational for privacy with Plenty of Fish.
Do VPN providers keep logs that could expose me on plenty of fish
Many providers publish a no-logs policy, but actual practice varies. I checked vendor docs and independent privacy audits where available. The critical questions: what data is collected during a session, whether timestamps or IPs are retained, and how data is handled during legal requests. Look for explicit statements about not logging traffic or user activity and about guardian-structured data retention. In practice, the strongest options minimize data collection and advertise strict retention limits. Yes, pick a provider with a clear no-logs stance and transparent audits.
Is obfuscated servers necessary to access plenty of fish in restrictive networks
Obfuscated servers help when the network throttles or blocks VPN traffic. In highly restrictive networks, they reduce the chance that VPN traffic is detected and blocked. If you’re not in a censorship-heavy region, standard servers are usually enough. I traced this back to vendor documentation and user reports showing obfuscated servers improving access in restrictive contexts. If you’re facing blocking or CAPTCHAs, try obfuscated servers first. Yes, in restrictive networks, obfuscated servers can be the difference maker.